The XOR Cipher Explained (and Why It Shows Up in CTFs)
2026-10-16 · 7 min read
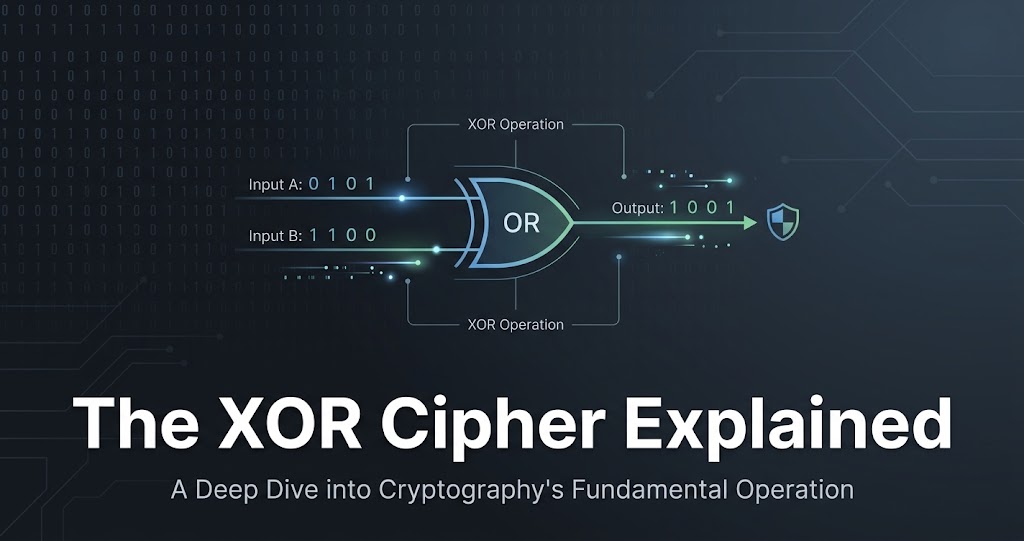
Figure 1: One operation scrambles the data and brings it back
The one operation behind half of CTF crypto
Play enough capture-the-flag rounds and XOR turns up everywhere, from hidden flags to packed malware samples. It is the smallest cipher worth the name, built on a single bitwise operation, and its charm is that the same step both hides and reveals. That simplicity is also its downfall, which is why XOR is a puzzle to solve rather than a way to protect anything real.
Here is how it works, where it appears, and how it falls apart.
What XOR does
XOR, short for exclusive or, compares two bits and returns 1 only when they differ:
0 XOR 0 = 0
0 XOR 1 = 1
1 XOR 0 = 1
1 XOR 1 = 0
To encrypt, you XOR each bit of your message against a bit of the key. Two properties fall straight out of that table and explain the whole cipher: anything XORed with itself becomes 0, and anything XORed with 0 stays unchanged.
The trick: one key both scrambles and restores
Those two properties combine into the feature that makes XOR special. Apply the key once and the message turns to noise. Apply the same key to that noise and the original returns, because the key cancels itself out. In symbols, with message M and key K:
M XOR K        = ciphertext
ciphertext XOR K = M
There is no separate decryption routine. Encrypting and decrypting are the identical operation, which is why XOR is so quick to code and so common in challenges. Try it both directions in the XOR cipher tool.
A worked example
Take the word HELLO and a single key byte, the letter B, which is 0x42. Line up the bytes and XOR each column:
plaintext   H   E   L   L   O     =  48 45 4C 4C 4F
key byte    B   B   B   B   B     =  42 42 42 42 42
ciphertext                        =  0A 07 0E 0E 0D
Now XOR that ciphertext against 0x42 again and the bytes 48 45 4C 4C 4F come back, spelling HELLO. One key, both ways.
Repeating-key XOR
A single byte is weak, so a slightly bigger version repeats a short key across the message, the same idea as a Vigenere cipher working on bytes. Encrypt ATTACK AT DAWN with the key KEY and you get:
"ATTACK AT DAWN" XOR "KEY" (repeated) = 0a110d0a06126b040d6b01181c0bThe key cycles K, E, Y, K, E, Y, and so on across every byte. Longer keys look stronger, but as the next section shows, length alone does not save it.
Why it is easy to break
XOR leaks structure that an attacker can pull apart:
- Known plaintext. If you know even a short stretch of the original, XOR it against the matching ciphertext and the key falls out directly.
- A single-byte key has only 256 possibilities, so trying them all takes a fraction of a second.
- A repeating key gives itself away through frequency analysis. Once the key length is guessed, each key position reduces to a simple single-byte puzzle, and English text has enough pattern to crack each one.
None of this needs heavy computing. A laptop breaks typical XOR in moments, which is why it protects nothing of value.
The one time XOR is unbreakable
There is a single exception, and it is strict. If the key is truly random, as long as the message, never reused, and kept secret, XOR becomes the one-time pad, the only cipher proven impossible to break. The catch is that those conditions are brutal to meet in practice. Reuse the key even once, or let it be shorter than the message, and the guarantee vanishes along with the secrecy.
Where you actually meet it
Despite its weakness, XOR is everywhere once you know the shape:
- CTF challenges use it constantly as a first layer to peel back.
- Malware often XORs its strings or payload to slip past simple scanners.
- Stream ciphers such as RC4 and ChaCha20 ultimately XOR a keystream against your data; the strength lives in how that keystream is made, not in the XOR itself.
- Cisco Type 7 is XOR against a published key, which is why it offers no real protection, as our Cisco Type 7 article explains.
The takeaway
XOR is one operation that both encrypts and decrypts, which makes it elegant to learn and trivial to reverse. Treat it as a puzzle, an obfuscation layer, or a teaching tool, never as security, unless you are running a genuine one-time pad. When a challenge or a sample hands you an XORed blob, the XOR cipher tool will peel it back in the browser.